
Where do you start with ISO 27001? With the policy? With the risk assessment? Or with buying a tool? Many organizations start somewhere in the middle, and that’s typically where projects get stuck.
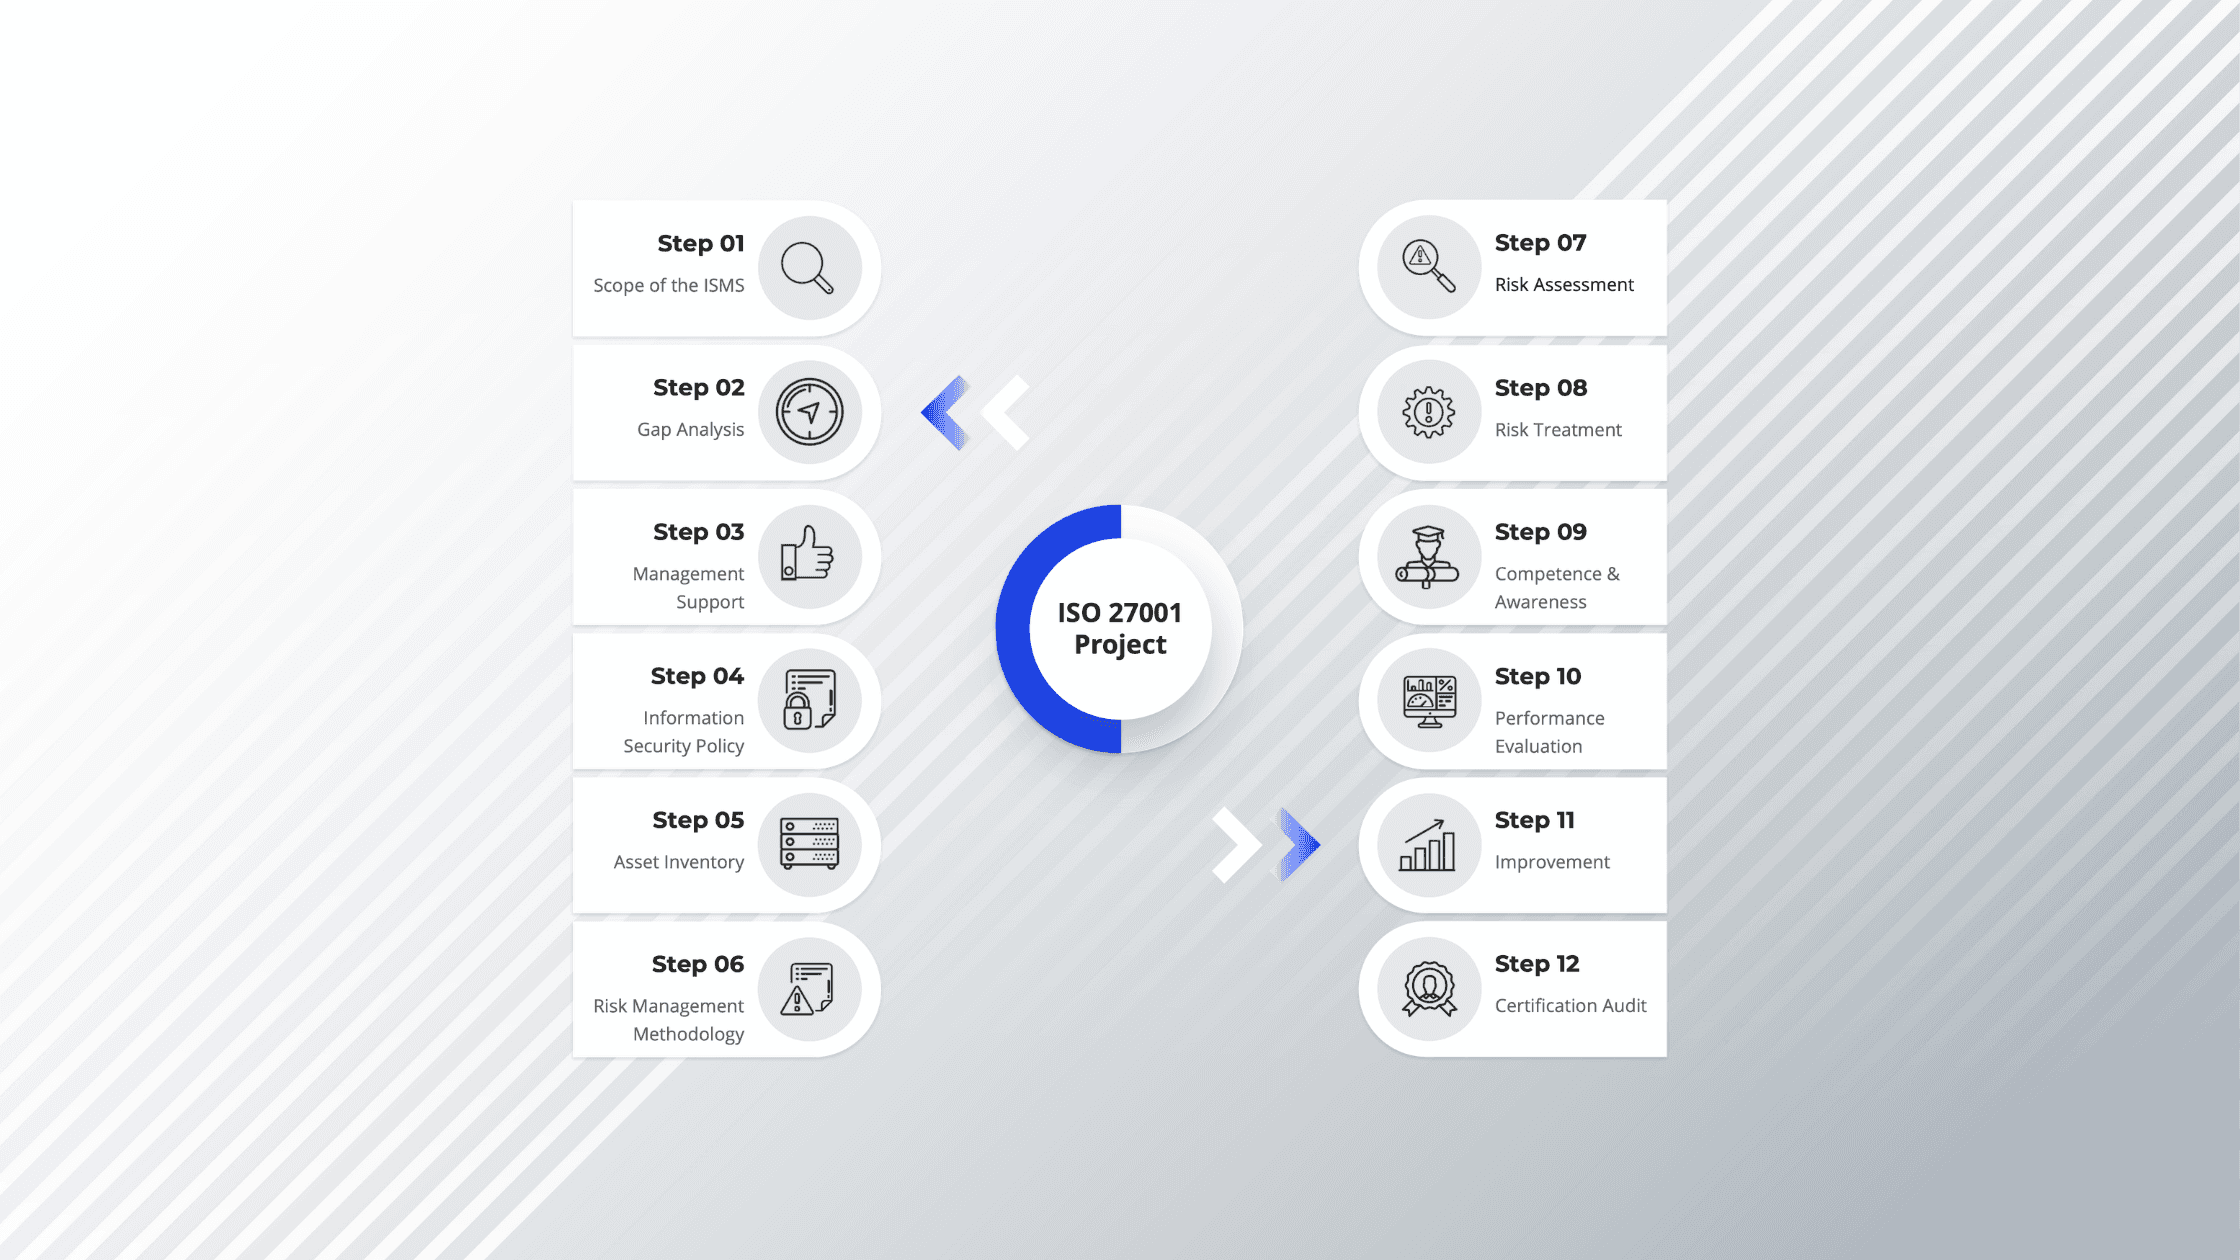
This guide walks you through the 12 steps in the order that works, from the scope of your ISMS to the certification audit. They follow the order in which the results build on each other, and they work for any organization, whatever its size or industry. Each step links to its own article with the requirements, a worked example and the tasks for your project.

What you’re building: an audit-ready ISMS
When is an ISMS project actually done? When the certificate arrives? Not quite. The certificate is issued by the certification body. What you deliver is an ISMS that’s ready for the audit, and it has four parts.

The requirements are met. I’ve counted 234 individual requirements in ISO 27001: 141 in clauses 4 to 10, and the 93 Annex A controls you compare your own controls with. Every one of the 141 has to be met, because none of them can be excluded.
The controls are in place. In stage 2 of the certification audit, the auditor checks three things: that your controls come from your risk assessment and risk treatment, that the controls, the Statement of Applicability, the risk results and your objectives fit together, and that the controls you say are implemented really are, and work. If your Statement of Applicability says multi-factor authentication is in place for all accounts, the auditor might simply open the admin console and check.
The evidence is available. That’s your documented information: what ISO 27001 requires, from the scope to the results of corrective actions, and what you’ve decided you need, like a backup procedure. Once you’ve decided you need it, it’s just as mandatory.
The evidence is a list.
Get the whole list.
All 143 documents and records an auditor expects: the 19 ISO 27001 requires and the 124 more auditors typically ask for, each mapped to its clause or Annex A control.

And the ISMS is in operation. Its processes are running, and it has already gone through its own checks at least once: an internal audit and a management review. A certification body won’t certify an ISMS that only exists on paper.
The 12 steps mapped to the standard
Step | Focus | Main reference |
|---|---|---|
1 | Scope of the ISMS | Clauses 4.1 to 4.4 |
2 | Gap analysis | Project preparation |
3 | Management support | Clauses 5.1, 5.3, 7.1 |
4 | Information security policy | Clauses 5.2, 6.2, 7.4 |
5 | Asset inventory | Control A.5.9 |
6 | Risk management methodology | Clause 6.1.2 |
7 | Risk assessment | Clauses 6.1.2, 8.2 |
8 | Risk treatment | Clauses 6.1.3, 8.3 |
9 | Competence and awareness | Clauses 7.2, 7.3 |
10 | Performance evaluation | Clauses 9.1 to 9.3 |
11 | Improvement | Clauses 10.1, 10.2 |
12 | Certification audit | Stages 1 and 2 |
Step 1: Scope of the ISMS
Before you can protect anything, you need to be clear about what you’re protecting. You determine the boundaries of the ISMS from your context, the requirements of your interested parties and the interfaces with other organizations. A clear scope keeps the project focused, and it’s exactly what the gap analysis in Step 2 will assess. Read how to define the ISO 27001 scope.
Step 2: Gap Analysis
Now you assess where you stand against the requirements of ISO 27001, within your scope. The standard doesn’t require a gap analysis, but it gives you an honest picture of what’s in place and what’s missing, and the facts you need in Step 3: what it takes and what it costs. Read how to run a gap analysis.
Step 3: Management Support
With the gap analysis in hand, you build a business case and a project charter, and top management commits the budget, the people and the mandate. That’s clauses 5.1, 5.3 and 7.1, and every later step depends on it. Read how to win management support.
Step 4: Information Security Policy
Top management establishes the information security policy, with your objectives or the framework for setting them, and you decide how you communicate. It’s the top of your documentation pyramid, and everything that comes after has to be consistent with it. Read how to write the information security policy.
Step 5: Asset Inventory
You identify the information and other associated assets within your scope, together with their owners. You can’t assess the risks to something you haven’t identified, so the inventory is the basis for your risk assessment. Read how to build the asset inventory.
Step 6: Risk Management Methodology
Before you assess any risks, you define how you’ll do it: your risk acceptance criteria and the criteria for performing risk assessments, so that the results stay consistent and comparable when you repeat them. Read how to define the risk methodology.
Step 7: Risk Assessment
Now you put the methodology to work. You identify, analyze and evaluate your information security risks and record them in a risk register. The results are mandatory documented information, and the basis for deciding what to do about each risk. Read how to conduct the risk assessment.
Step 8: Risk Treatment
You decide how to treat each risk, determine the necessary controls, compare them with the 93 controls of Annex A and produce your Statement of Applicability. Then you implement the risk treatment plan. Step 8 is typically the largest and most time-consuming step, because this is where most of the actual security work happens. Read how to create the risk treatment plan.
Step 9: Competence & Awareness
An ISMS is only as strong as the people operating it. You make sure that everyone whose work affects the ISMS has the competence for it, and that everyone knows the policy, their role and the consequences of not following it. It comes after risk treatment on purpose, so that training targets the risks and controls you’ve actually chosen. Read competence and awareness requirements.
Step 10: Performance Evaluation
You monitor and measure whether the ISMS achieves what it should, you run an internal audit, and top management reviews the ISMS in a management review. That’s what puts your ISMS into operation, the fourth part of an audit-ready ISMS. Read performance evaluation explained.
Step 11: Improvement
The results of the performance evaluation, and any nonconformities you find along the way, lead to corrections and corrective actions. With that, your ISMS has gone through the whole cycle once. Read nonconformity and corrective action.
Step 12: Certification Audit
Now you’re ready, and you choose a certification body. Stage 1 reviews your documentation and readiness, stage 2 how the ISMS works in practice. And if you decide not to seek certification, Steps 1 to 11 work exactly the same way. Read the certification audit explained.
At Barvello: ten months from start to audit
Barvello Coffee Systems is the fictional company of our ISO 27001 Lead Implementer course: a family-owned maker of professional coffee machines in Munich, with about 500 employees and its own cloud platform, Barvello Connect. On 5 October 2026, the management board decided to seek ISO 27001 certification by 30 September 2027, three months before the framework agreement with its key customer Ovena expires.

Nadia Berger started as project lead on 2 November 2026 and built her plan with the project plan from the ISO 27001 Toolkit. The scope proposal is due at the management meeting on 14 December, the gap analysis by 22 January, and the business case goes to the advisory board on 3 February 2027. Then come six months of implementation, from February to July, covering Steps 4 to 11. And in August and September, the certification audit. That’s about ten months from start to audit. Ambitious, but doable, if management backs the project.
Her definition of done is the four parts above. All 141 requirements are met, and for many of them, like document control, internal audits and the management review, Barvello can build on its ISO 9001 system. Every control traces back to a risk, like multi-factor authentication for all Microsoft 365 accounts. The evidence is in place, from the scope to the Statement of Applicability. And the ISMS has run, with an internal audit in June and a management review in July 2027.
Watch the full lecture above. It’s “The 12 Steps to an Audit-Ready ISMS” from the course, with every step and Barvello’s plan.
How long does implementation take?
Duration depends on scope size, existing maturity and how much time the responsible people can actually dedicate. As orientation: small organizations with a focused scope commonly need three to six months, mid-sized organizations six to twelve.
One constraint is fixed and often overlooked: the ISMS must have operated before the certification audit. ISO/IEC 27006, the standard for certification bodies, expects evidence that internal audits and management reviews are implemented and effective before an ISMS can be certified.

So plan for at least the internal audit, the management review and a few months of routine records before the certification audit.
From the auditor’s chair
The most expensive mistake I see is sequence inversion: organizations buy and configure controls first, then write a risk assessment that justifies the purchases. The standard runs the other way, and the audit trail shows the difference. When the risk assessment references controls by their marketing names, or every identified risk happens to be treated by something already owned, the methodology loses credibility and stage 2 becomes uncomfortable. Follow the order: understand, decide, then implement.
Frequently asked questions
Do we need a consultant to implement ISO 27001?
No. The standard does not require external support. What it requires is competence, and clause 7.2 lets you build it internally. Many organizations implement with an internal lead who has been trained for the role.
Do all 93 Annex A controls apply to us?
Not necessarily. Applicability is decided through risk treatment and documented in the Statement of Applicability, with a justification for every inclusion and exclusion.
Can we change the order of the steps?
Within limits. Some dependencies are fixed: the scope precedes everything, the methodology precedes the assessment, and the assessment precedes treatment. The order in this guide reflects those dependencies.
Do we need the certificate to benefit from the 12 steps?
No. Steps 1 to 11 build the ISMS, and they work exactly the same way whether or not you seek certification in Step 12.
From roadmap to execution
Knowing the 12 steps is the easy part. The hard part is execution: breaking each step into concrete tasks, producing the documents an auditor expects, and keeping the project moving without losing weeks to a blank page or a missed requirement. This is also where judgment matters most. AI can draft a policy in seconds, but it can’t scope your ISMS, defend your control selection to an auditor, or tell you whether its own output fits your organization.
Our ISO/IEC 27001 Lead Implementer course turns this roadmap into a working project. It follows the same 12 steps: for each one, you learn what the standard requires, watch the step carried out at Barvello, and then apply it to your own organization with the ISO 27001 Toolkit, a project plan with 400+ sequenced tasks and templates for every deliverable. The course is part of GRCLab+, which also gives you a weekly live Q&A with a practising ISO 27001 Lead Auditor.
The 12 steps in the course.
Watch Barvello go all the way.
Chapter 3 (5 lectures, 21 min) shows you what an audit-ready ISMS looks like, how to handle documented information and the 12 steps. Then every step follows the same pattern: the requirements, Barvello’s case study and your tasks in the project plan.
The Project Goal: An Audit-Ready ISMS
06:39
Clause 7.5 Documented Information
06:14
The 12 Steps to an Audit-Ready ISMS
04:57
Template: ISO 27001 Project Plan
400+
Ready to start? Each of the 12 steps has its own article in this guide. Start with Step 1: Scope of the ISMS.
