Bestseller

Created by Aron Lange
English
4.7
4,795+ ratings
25,100+
students enrolled
TRECCERT
approved Trainer


CERTIFICATION


If you are leading an ISO 27001 project, you are fighting a battle against the clock. The standard tells you what must be done. The how is left entirely to your imagination.
That leaves you staring at a blank map, forced to build an ISMS from scratch while the deadline moves closer.
This course closes that gap with a complete system. A 12-step roadmap takes you from defining the scope of your ISMS to the certification audit, so you always know the next move. A project plan breaks every step into 400+ tasks with owners and milestones, so progress is visible. Pre-built templates give you the deliverables an auditor expects. And 12 hours of video lessons show you how to build each one, and why the requirement exists, so you can defend it when the auditor asks. All of it ships with the course as the ISO 27001 Toolkit.
The destination is not only a passed audit. Everything you learn feeds directly into the ISO/IEC 27001 Lead Implementer exam. You sit the practice exam when you feel ready, then book the real one. With the Certification Bundle, the voucher is already in your inbox, with a free retake behind you if you need it.
How the course works
The course follows the 12 steps of a real ISO 27001 implementation project, from the scope of your ISMS to the certification audit.
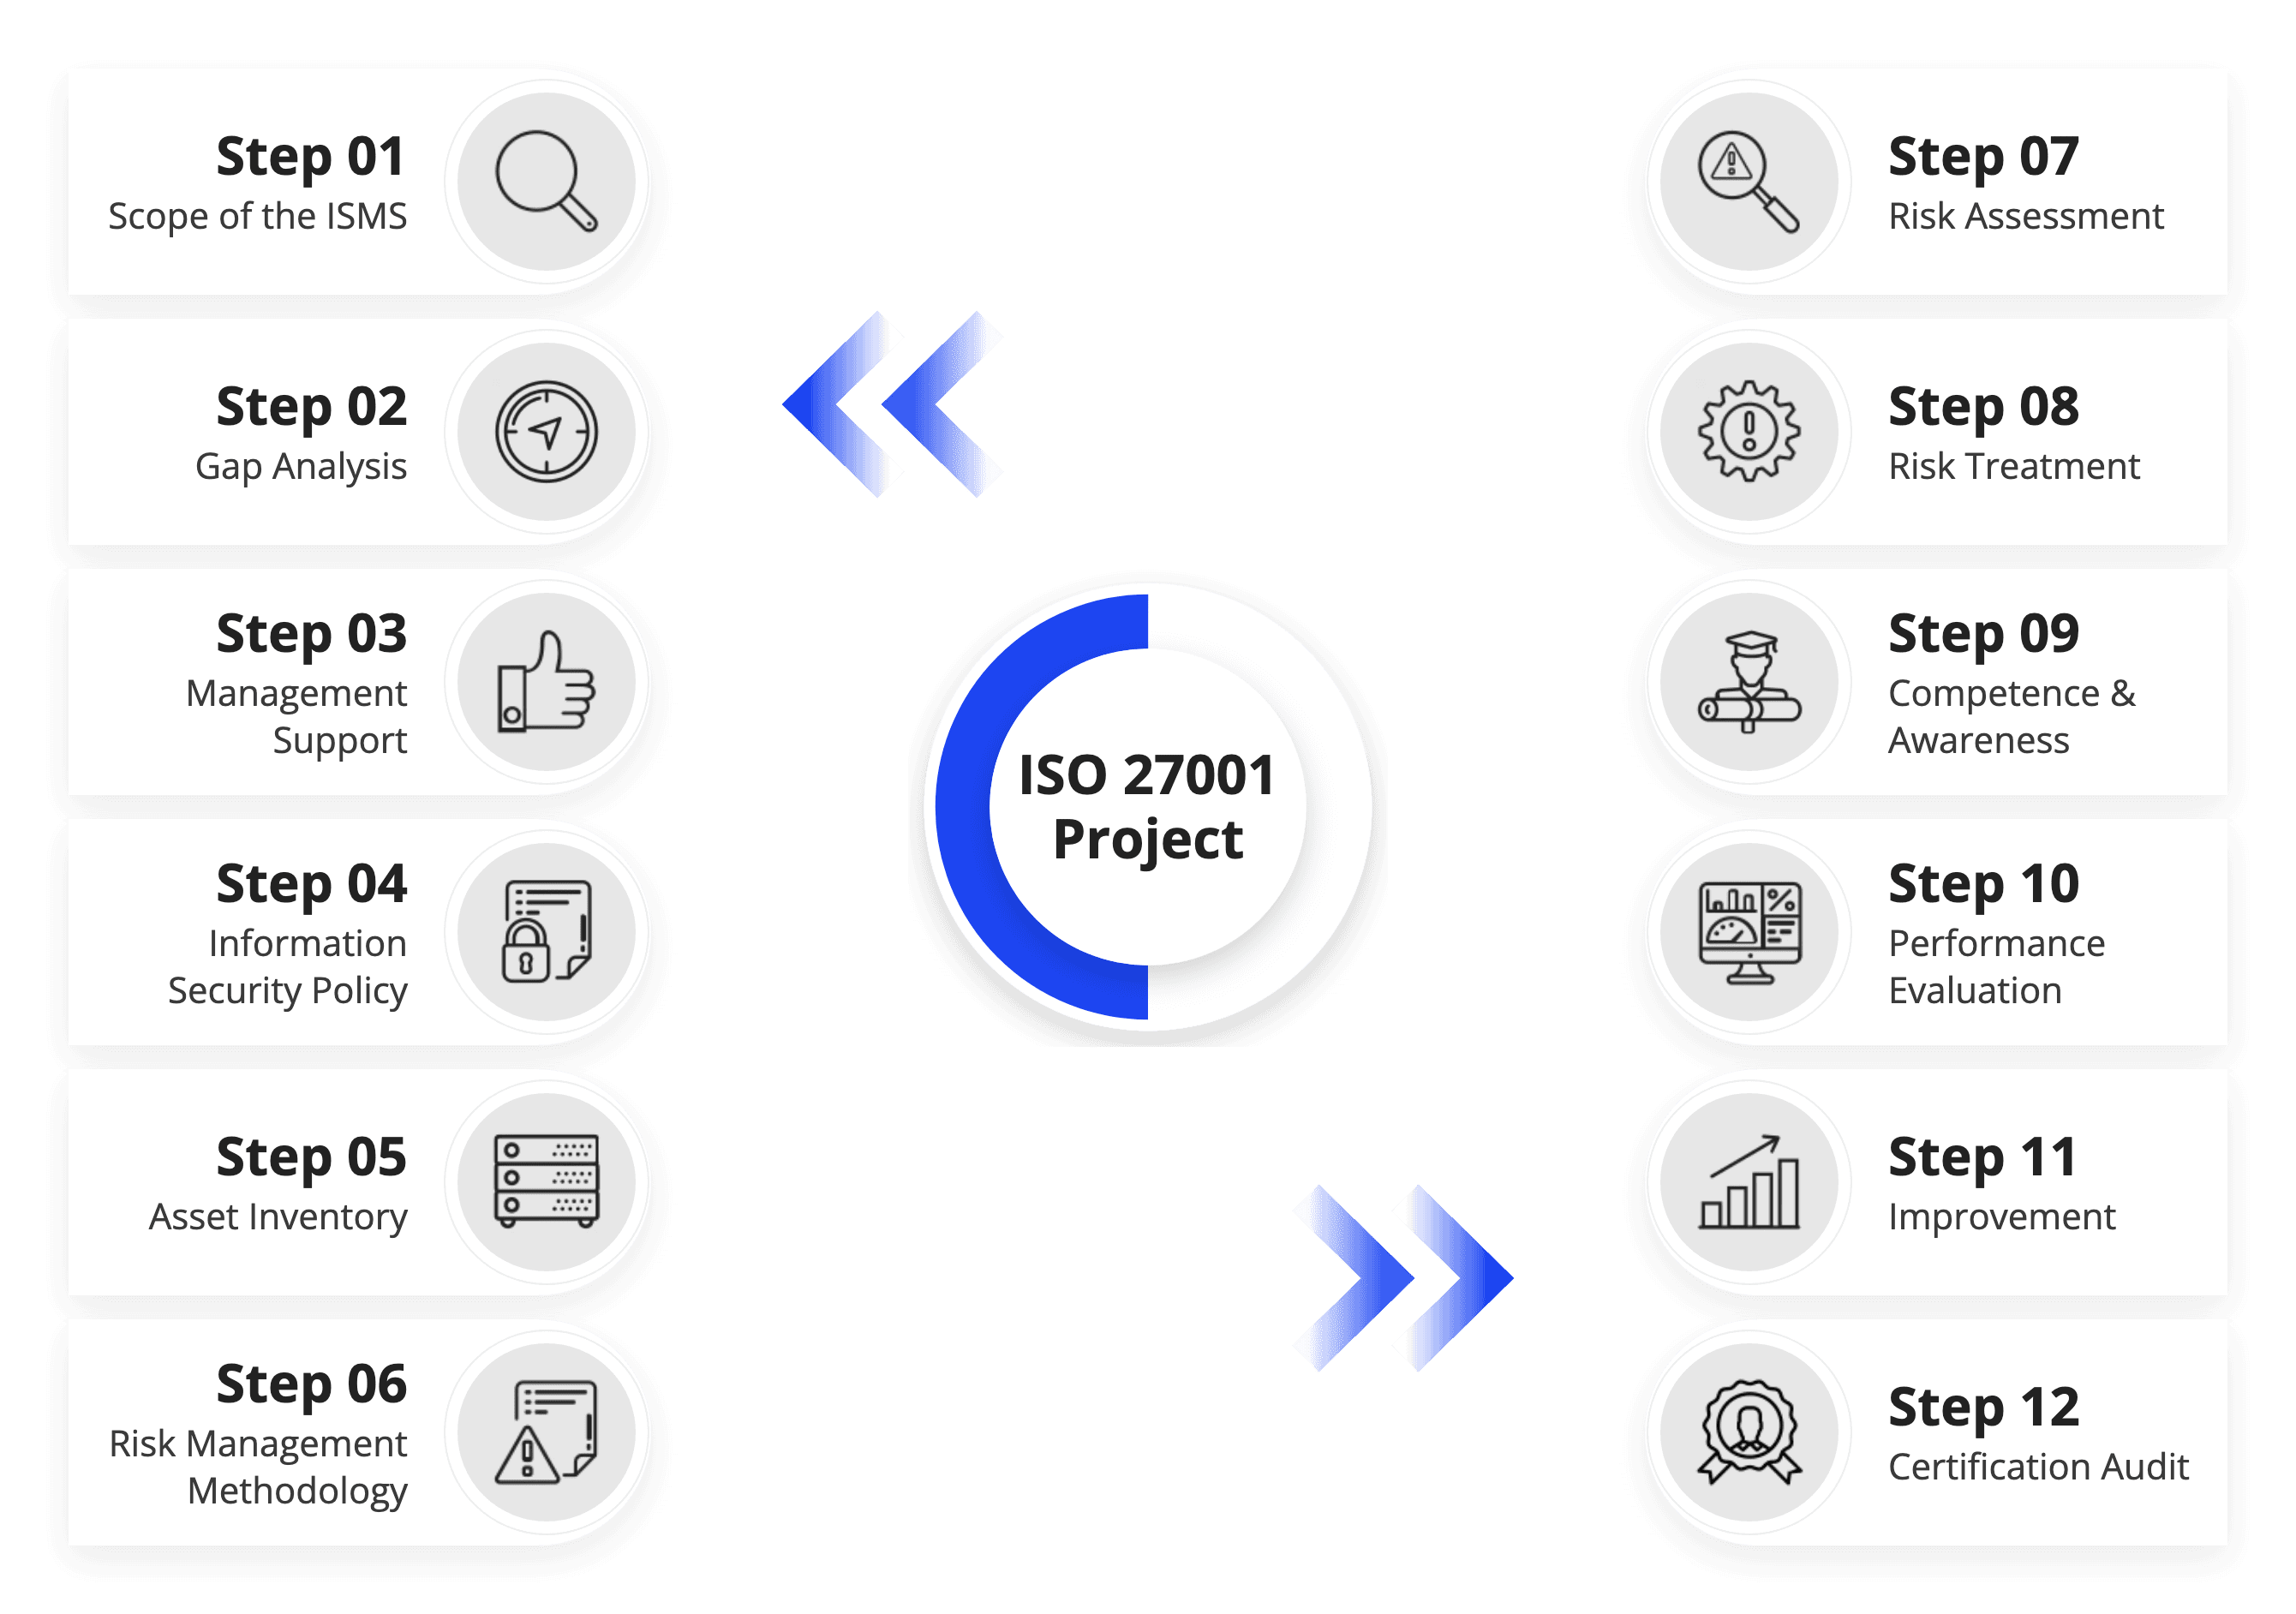

Every step works the same way
Three parts per step, so you always know what comes next.
01 · LEARN

Requirements
What ISO/IEC 27001 requires in this step, and why, so you have an answer when the auditor asks.
02 · WATCH

Case Study
The step carried out at Barvello with the real templates: decisions, documents, approvals.
03 · APPLY

Your Turn
The same step for your organization, with the project plan and templates from the ISO 27001 Toolkit.
CASE STUDY
Meet Barvello Coffee Systems.
A family-owned maker of professional coffee machines from Munich. Its largest customer makes ISO/IEC 27001 a condition for renewing their contract, and ISMS project lead Nadia Berger has less than a year to get there. You follow her through every step.


Case Dossier Included
The company at a glance: history, products, customers, locations and organization. Your starting point for every step of the case study.
COURSE
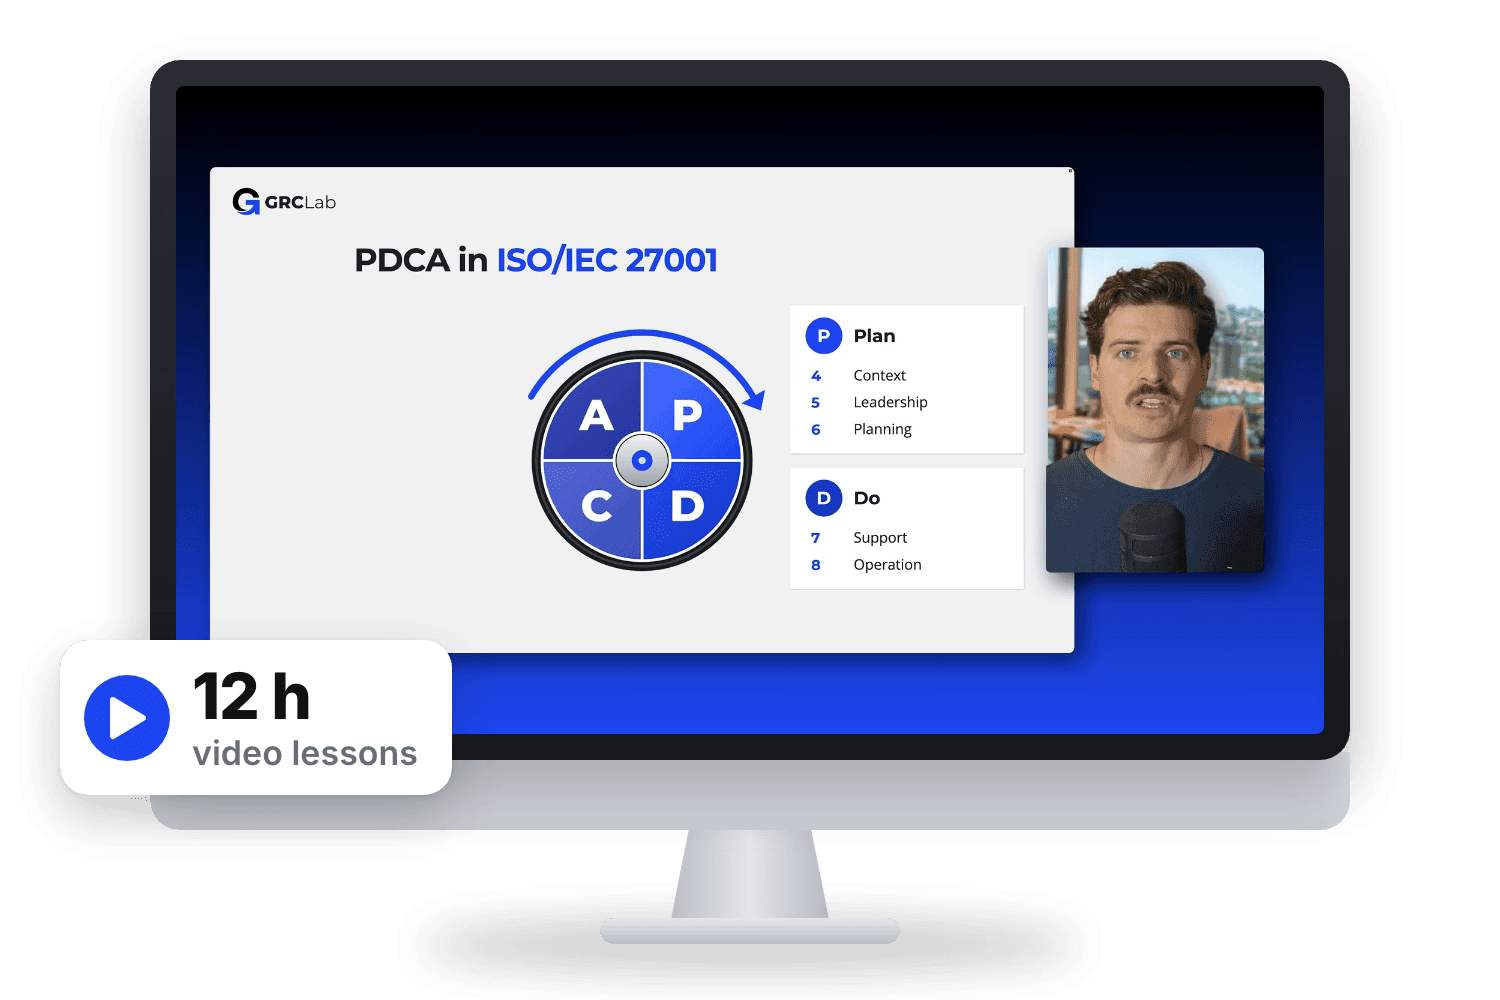
Video Training
12 hours of video, from the foundations to the certification audit. In every step, you apply what you've learned to your own organization.

TOOLKIT
ISO 27001 Toolkit
A project plan with more than 400 tasks across all 12 steps, plus templates for policies, procedures, processes and records.

LIVE
Weekly Live Q&A
Every week, bring your questions to a live session with Aron Lange, a practising ISO 27001 Lead Auditor. Get answers from someone who audits management systems for a living.

EXAM
Practice Exam
150 questions in the format of the TRECCERT exam, with an explanation for every answer option, so you know why an answer is right or wrong.

VOUCHER
Exam Voucher with Free Retake
With the Certification Bundle you get the official certification exam voucher plus a free retake: a second chance at no additional cost.

STUDY GUIDE
Official Study Guide
Included in the Certification Bundle: the extensive official TRECCERT study guide covers everything you need to pass the exam.
Inside the ISO 27001 Toolkit
Everything you need to run your implementation project, from the first task to the certification audit. The same files you see in action in the case study, ready to adapt to your organization.
PROJECT PLAN
Always know what comes next.
The 12 steps of the course as a ready-made project plan in Excel. Plan your dates, assign the tasks and track your progress.

All 12 steps, broken down into more than 400 tasks
Tasks linked to their ISO/IEC 27001 clause or Annex A control
Durations, milestones and a Gantt chart for your timeline
Every deliverable linked to its template
Templates for every deliverable
Four types, colour-coded and numbered like in the plan.

POL
Policies
e.g. Information Security Policy, Access Control Policy

SOP
Procedures
e.g. Risk Assessment Procedure, Internal Audit Procedure

PRO
Processes
e.g. Risk Assessment Process, Management Review Process

REC
Records
e.g. ISMS Scope, Statement of Applicability
+
Plus: mind maps of ISO/IEC 27001, 27002, 27005 and the ISO 27000 family, and a control mapping from Annex A to NIST SP 800-53, the NIST CSF and the CIS Controls.

LIVE
Course Introduction
4 lectures
•
16min
Course Resources
2 lectures
•
6min
Chapter 1: Information Security Fundamentals
8 lectures
•
35min
Chapter 2: ISO/IEC 27001:2022
8 lectures
•
51min
Chapter 3: Implementation Project
5 lectures
•
21min
Step 1: Scope of the ISMS
9 lectures
•
44min
Step 2: Gap Analysis
1 lecture
•
4min
Step 3: Management Support
6 lectures
•
34min
Step 4: Information Security Policy
8 lectures
•
27min
Step 5: Competence & Awareness
6 lectures
•
19 min
Step 6: Inventory of Assets
6 lectures
•
22min
Step 7: Risk Management Methodology
12 lectures
•
45min
Step 8: Risk Assessment
5 lectures
•
11min
Step 9: Risk Treatment
9 lectures
•
29min
Step 10: Performance Evaluation
7 lectures
•
29min
Step 11: Improvement
5 lectures
•
21min
Step 12: Certification Audit
3 lectures
•
9min
Annex A: 5. Organizational Controls
37 lectures
•
1hr 18min
Annex A: 6. People Controls
9 lectures
•
45min
Annex A: 7. Physical Controls
15 lectures
•
1hr 16min
Annex A: 8. Technological Controls
34 lectures
•
1hr 13min
Practice Exam
1 lectures
•
3min




Lirim Bllaca
COO @ TRECCERT


